Australia
 Singapore
 Philippines
 India
7.22 MIN READ
Compliance and Cybersecurity Challenges Facing Australia’s NFP Industry
 Niten Devalia | Sep 18, 2026
Donor details, beneficiary records, volunteer information, employee data, financial records, health information and case files are increasingly stored and managed through digital platforms.
At the same time, NFPs are adopting cloud applications, Microsoft 365, online fundraising platforms, CRM systems and digital service delivery to improve efficiency and reach more people.
This creates an important challenge: how can NFPs embrace digital transformation while protecting the people, data and trust they depend on?
For resource-constrained organisations, building the right balance between compliance, security and affordability is essential.
Why Cybersecurity Matters for NFPs
NFPs can be attractive targets because they often hold valuable personal and financial information while operating with limited technology resources.
A successful cyberattack can result in:
- Financial loss
- Data breaches
- Service disruption
- Loss of donor confidence
- Reputational damage
- Harm to beneficiaries and communities
For an organisation built around community trust, the consequences can extend well beyond the immediate technical impact.
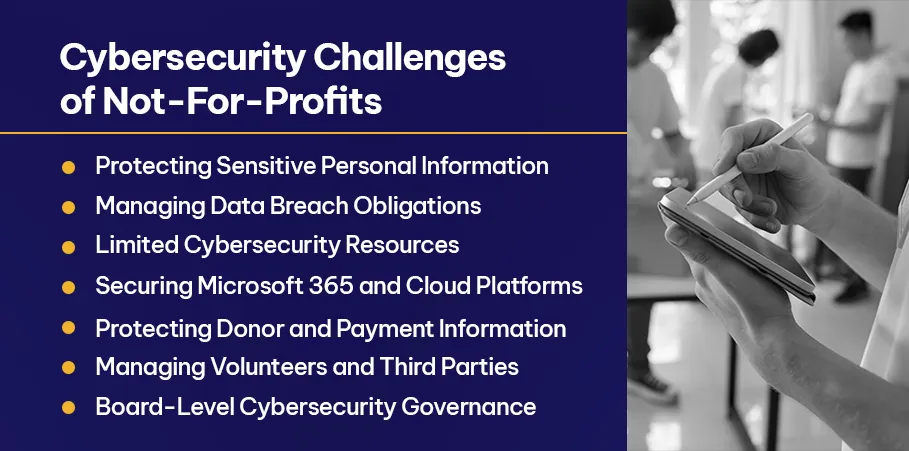
Challenge 1: Protecting Sensitive Personal Information
NFPs may collect significant amounts of personal and sensitive information from donors, beneficiaries, members, volunteers and employees.
Depending on the organisation and its activities, privacy obligations can apply to how this information is collected, stored, used and disclosed.
NFPs should therefore understand:
- What information they collect
- Why they collect it
- Where it is stored
- Who can access it
- How long it is retained
- When it should be securely deleted
Good data governance provides the foundation for both privacy and cybersecurity.
Challenge 2: Managing Data Breach Obligations
A cyber incident can quickly become a compliance issue when personal information is compromised.
NFPs should therefore have a documented data breach response process covering:
- Detection and escalation
- Initial assessment
- Containment
- Investigation
- Notification
- Recovery
- Post-incident review
Having a plan before an incident occurs can significantly improve the organisation’s ability to respond effectively.
Challenge 3: Limited Cybersecurity Resources
One of the biggest challenges facing NFPs is balancing cybersecurity investment with their broader mission.
Many organisations operate with:
- Small IT teams
- Limited security expertise
- Restricted budgets
- Volunteer-based operations
- Multiple technology platforms
This can make it difficult to maintain specialist capabilities internally.
The answer is not necessarily to implement every available security technology. Instead, NFPs should prioritise controls that address their most significant risks.
Challenge 4: Securing Microsoft 365 and Cloud Platforms
Cloud platforms have become essential for many NFPs.
Microsoft 365 enables teams to collaborate, communicate and access information remotely, but incorrect configurations can expose sensitive data.
Common risks include:
- Excessive user permissions
- Weak identity controls
- Unsecured SharePoint sites
- Unmanaged devices
- External file sharing
- Poorly configured email security
Strong identity and access controls, MFA, Conditional Access and appropriate data governance can help reduce these risks.
Challenge 5: Protecting Donor and Payment Information
Fundraising is a critical source of revenue for many NFPs.
Online donations, recurring payments and fundraising campaigns create additional cybersecurity considerations.
Attackers may attempt to:
- Redirect payments
- Compromise donor accounts
- Conduct phishing attacks
- Steal payment information
- Impersonate employees or executives
NFPs should ensure financial systems are protected through strong authentication, access controls, monitoring and appropriate segregation of duties.
Challenge 6: Managing Volunteers and Third Parties
NFPs often rely on volunteers, contractors, technology providers and partner organisations.
This creates additional access and governance challenges.
A volunteer who leaves the organisation, for example, should not retain access to systems or sensitive information.
Organisations should establish processes for:
- Onboarding users
- Granting appropriate access
- Reviewing permissions
- Removing access promptly
- Managing third-party accounts
The principle of least privilege should guide access decisions: users should only receive the access required to perform their role.
Challenge 7: Board-Level Cybersecurity Governance
Cybersecurity should not sit entirely with the IT team.
Boards and leadership teams should understand:
- Major cyber risks
- Critical systems
- Sensitive information
- Current security posture
- Incident response arrangements
- Third-party risks
Regular reporting helps turn cybersecurity from a technical issue into an organisational risk management priority.
Building a Practical Cybersecurity Framework
NFPs do not need to solve every cybersecurity challenge at once.
A practical approach starts with understanding the organisation’s highest risks and establishing strong fundamentals.
Key priorities include:
-
Strengthen Identity
Implement MFA, secure administrator accounts, review permissions and remove unnecessary access.
-
Protect Endpoints
Keep operating systems and applications updated and use appropriate endpoint protection.
-
Secure Data
Classify sensitive information, control access and establish appropriate retention and deletion practices.
-
Maintain Reliable Backups
Regular backups help organisations recover from ransomware, accidental deletion and system failures.
-
Monitor Security
Continuous monitoring can identify suspicious activity earlier and improve incident response.
-
Test Incident Response
An incident response plan should be documented, communicated and periodically tested.
Compliance Should Enable Trust, Not Just Check Boxes
For NFPs, compliance is closely connected to trust.
Donors need confidence that their contributions are protected. Beneficiaries need assurance that their personal information is handled responsibly. Volunteers and employees need secure systems. Boards need confidence that organisational risks are being managed appropriately.
This means compliance should be embedded into everyday processes rather than treated as an annual exercise.
Strong governance, data protection and cybersecurity work together to create a more resilient organisation.
Why Choose Exigo Tech as Your Managed Intelligence Partner
At Exigo Tech, we help Australian NFPs strengthen cybersecurity, protect sensitive information and build technology environments that support their mission.
As your Managed Intelligence Partner, we provide:
- NFP Cybersecurity Assessments
- Managed Security as a Service (MSaaS)
- Microsoft 365 Security
- Microsoft Entra ID and Identity Security
- Essential Eight Assessments
- Data Governance and Protection
- Microsoft Purview
- Backup and Disaster Recovery
- Ongoing Managed IT and Cybersecurity Services
Our approach helps NFPs improve security and compliance without adding unnecessary complexity to already resource-conscious environments.
Protecting Your Mission Starts with Protecting Your Data
For Australia’s NFP sector, cybersecurity is ultimately about protecting people and preserving trust.
As organisations become increasingly dependent on cloud platforms and digital services, cybersecurity and compliance must evolve alongside them.
By strengthening identity security, protecting sensitive information, improving governance, preparing for data breaches and adopting a risk-based cybersecurity framework, NFPs can build greater resilience without losing focus on their core mission.
The goal is not simply to comply with requirements. It is to create a secure technology foundation that allows NFPs to serve their communities with confidence.

 Exigo Tech - Ask AI (Beta)