Australia
 Singapore
 Philippines
 India
7.05 MIN READ
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
 Niten Devalia | Oct 21, 2026
Healthcare providers rely on digital systems for almost every part of their operations. Patient records, clinical communications, appointment information, financial data and internal collaboration increasingly move through cloud platforms such as Microsoft 365.
That connectivity improves productivity and accessibility, but it also creates security responsibilities. A compromised account, misconfigured sharing permission or phishing attack can expose sensitive information and disrupt critical services.
For healthcare organisations, Microsoft 365 security is therefore not simply an IT concern. It is part of protecting patient privacy, maintaining operational continuity and meeting regulatory obligations.
Why Microsoft 365 Security Matters in Healthcare
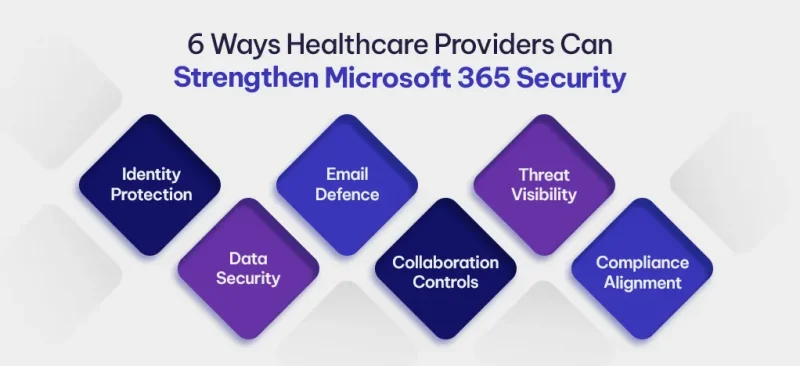
1. Protect Healthcare Identities and User Accounts
Identity is one of the most important security controls in Microsoft 365.
Healthcare staff may have access to highly sensitive information, making compromised accounts a valuable target for attackers. Phishing, stolen credentials and session hijacking can allow attackers to access email, files and business applications.
Microsoft Entra ID can help healthcare organisations strengthen identity security through capabilities such as:
- Multi-factor authentication
- Conditional Access
- Risk-based identity protection
- Privileged access controls
- Strong authentication policies
- Access reviews
2. Secure Patient and Business Data
Healthcare data can exist across emails, SharePoint sites, OneDrive, Teams conversations and business applications.
Without appropriate controls, sensitive information can be accidentally shared with the wrong person or accessed more broadly than intended.
Microsoft Purview can support data security and compliance through capabilities including data classification, sensitivity labels, Data Loss Prevention (DLP) and information protection policies.
For healthcare providers, these controls can help identify and protect sensitive information while reducing the risk of accidental disclosure.
For example, policies can help prevent sensitive information from being shared through inappropriate channels or alert security teams when potentially risky activity occurs.
The objective is not simply to restrict data. It is to make sure information is available to the right people, in the right context, with appropriate controls around its use.
3. Strengthen Email Security Against Phishing
Email remains one of the most common entry points for cyberattacks.
Healthcare employees may receive appointment requests, invoices, referrals, supplier communications and other legitimate-looking messages every day. Attackers can exploit this volume and urgency to make phishing emails appear convincing.
Microsoft Defender for Office 365 can provide additional protection against threats such as:
- Phishing
- Malicious links
- Malicious attachments
- Business email compromise
- Impersonation attacks
- Other email-based threats
However, technology alone is not enough.
Healthcare organisations should combine email protection with user awareness, strong identity controls and processes for reporting suspicious messages.
A layered approach reduces the likelihood that a single compromised email account becomes the starting point for a wider incident.
4. Secure Microsoft Teams, SharePoint and OneDrive
Collaboration platforms can quickly become repositories for sensitive information.
Teams, SharePoint and OneDrive make it easier for healthcare teams to collaborate, but excessive permissions or poorly managed external sharing can introduce risk.
Security teams should regularly review:
- External sharing settings
- Guest access
- SharePoint permissions
- OneDrive sharing
- Teams membership
- Sensitive document access
- Dormant accounts and users
5. Improve Visibility and Threat Detection
Preventing every attack is unrealistic. Healthcare providers also need the ability to identify suspicious activity quickly and respond effectively.
Microsoft security technologies can provide visibility across identities, endpoints, email, applications and cloud environments.
Security teams can use this information to investigate unusual behaviour such as:
- Repeated failed authentication attempts
- Suspicious sign-ins
- Unusual file downloads
- Unexpected privilege changes
- Malicious email activity
- Unusual access from unfamiliar locations
For organisations with limited internal security resources, managed security services can extend this capability with continuous monitoring, threat detection and incident response.
The goal is to reduce the time between an attacker gaining access and the organisation identifying and containing the threat.
6. Build Security Around Compliance Requirements
Healthcare organisations must consider the privacy, security and regulatory requirements that apply to their operations.
In Australia, this can include obligations under the Privacy Act and Australian Privacy Principles, along with healthcare-specific requirements and contractual obligations depending on the organisation and services it provides.
Microsoft 365 security and compliance capabilities can support organisations in implementing appropriate controls, but technology should form part of a broader governance framework.
Healthcare providers should clearly define:
- What information is considered sensitive
- Who can access it
- Where it can be stored
- How it can be shared
- How long it should be retained
- How security incidents are handled
- How access and policies are reviewed
Good governance turns individual security tools into a coordinated security strategy.
Common Microsoft 365 Security Gaps in Healthcare
Even organisations with Microsoft 365 security features enabled can have gaps in their configuration.
Common issues include:
- MFA enabled inconsistently across users
- Excessive administrator privileges
- Uncontrolled external sharing
- Poorly configured Conditional Access
- Unmanaged devices accessing business data
- Inadequate DLP policies
- Limited visibility into suspicious activity
- Inactive accounts that remain enabled
- Lack of regular security reviews
- Security policies that do not reflect changing business requirements
These gaps often develop gradually rather than from one major mistake.
Regular Microsoft 365 security assessments can help identify configuration weaknesses before they become security incidents.
Why Choose Exigo Tech as Your Managed Intelligence Partner?
Healthcare security requires more than deploying security products. It requires an understanding of how technology, data, users and business processes interact.
As a Managed Intelligence Partner, Exigo Tech helps healthcare organisations strengthen their technology environment through a combination of cybersecurity, Microsoft 365, cloud, infrastructure, data and managed services expertise.
Our approach focuses on helping organisations:
- Protect sensitive information and identities
- Strengthen Microsoft 365 security controls
- Improve visibility across users, devices and data
- Support compliance and governance requirements
- Reduce security risks without creating unnecessary operational complexity
- Continuously optimise their technology and security environment
Where Microsoft 365 is part of the environment, we can help organisations make better use of capabilities across Microsoft security, identity, data protection and device management while integrating them into a broader security strategy.
 Exigo Tech - Ask AI (Beta)